Allow Only Approved AMIs in Terraform with OPA
An OPA policy that fails the Terraform plan when an EC2 instance uses an AMI that isn't on an approved list, with the list kept in an external JSON data file.
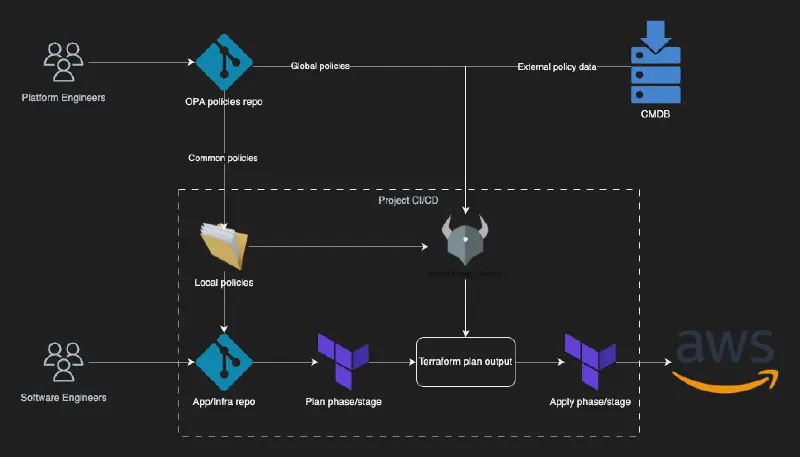
Enforcing AWS Resource Tags with OPA
Check a Terraform plan for required AWS tags and allowed values with OPA: common and per-environment rules, plus a whitelist of exempt resources.
Testing Terraform Plans with OPA and Conftest (and Atlantis)
A Rego policy that blocks S3 buckets with force_destroy in the Terraform plan, tested with the OPA CLI and Conftest and run in Atlantis or any CI pipeline.
How I Learned the Hard Way That Terraform Needs Policy as Code
Case study: a deleted Terraform state bucket forced a rebuild of 15 AWS accounts. How that incident became a policy-as-code guardrail that stops dangerous changes at plan time.
Shift-Left Cost Checks for Terraform with OPA and Terracost
Catch cloud cost problems before apply: OPA policies that block expensive resources in the Terraform plan, Infracost estimates and self-hosted Terracost on MySQL.